
In this article
Fraud Management Solution
A fraud management solution helps organisations detect, prevent, investigate, and report fraud across transactions, accounts, and digital channels. This guide explains what such a solution does, the capabilities to look for, implementation and operational considerations, deployment options, a buying checklist, KPIs to measure success, common pitfalls, and practical steps to build a resilient program. The tone here is calm, factual, and practical—aimed at risk, compliance, product, and operations teams.
Contents
What is a fraud management solution?
Why organisations need one
Core features and how they work
Benefits for business and operations
Deployment and architecture options
Implementation considerations
Operational playbooks and processes
Buying checklist
KPIs, ROI examples, and measurement
Common pitfalls and mitigation
Maintaining and evolving the program
Closing: choosing the right partner
What is a fraud management solution?
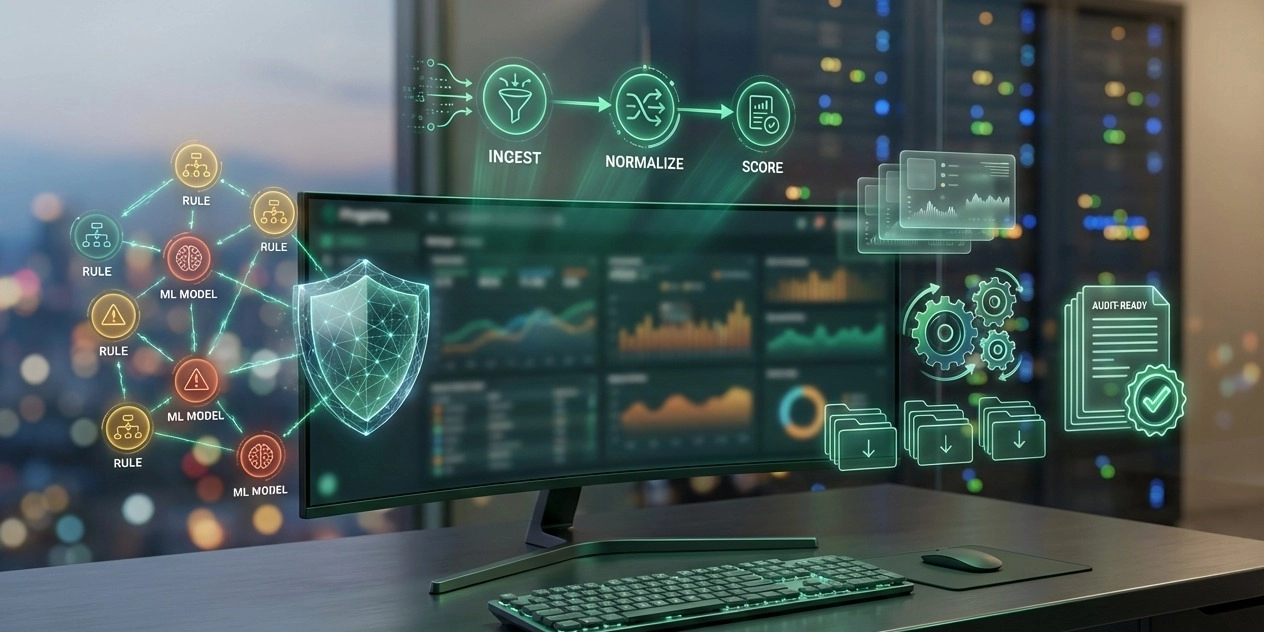
A fraud management solution is an integrated set of software, data pipelines, models, rules, and investigator tools designed to identify and stop fraudulent activity. It collects and normalises event data, scores risk using rules and models, furnishes investigators with contextual evidence, automates routine decisions, and produces audit-ready reports for compliance.
Fraud management overlaps with compliance disciplines such as anti-money laundering (AML) and know your customer (KYC). AML refers to processes that prevent proceeds of crime from being legitimised; KYC is the identity verification work done when onboarding and monitoring customers.
A mature solution blends automation and human oversight to reduce loss, maintain trust, and support regulatory obligations.
Why organisations need a fraud management solution
Fraudsters adapt quickly: new attack methods, automation, and cross-border channels create shifting risk. Manual approaches—spreadsheets, siloed alerts, and static rules—cannot keep pace. A consolidated fraud solution offers:
Timely detection through real-time event scoring.
Consistent decisioning across channels and products.
Tools for efficient investigation and case resolution.
Audit trails and reporting needed for regulators and auditors.
The ability to scale detection and operations without linear headcount increases.
When fraud is embedded in product flows (payments, onboarding, account changes), decision latency and integration quality directly affect losses and customer experience.
Core features and how they work
A complete fraud management solution combines multiple capabilities. Below are core features and why they matter.
Real-time detection and low-latency decisioning
Real-time detection evaluates events—transactions, logins, or account changes—as they occur. Low-latency decisioning is essential where user experience or payments would otherwise be disrupted by delays.
Common outcomes:
Automatically block or hold high-risk transactions.
Request step-up authentication (OTP, biometric challenge).
Allow low-risk actions to proceed frictionlessly.
Design note: balance speed with evidence. Over-blocking harms customers; under-blocking leaves exposure.
Machine learning and adaptive models
Machine learning augments rules by identifying complex or subtle patterns. Key practices:
Use supervised models trained on labelled fraud data, and unsupervised methods to surface anomalies.
Maintain retraining schedules to prevent model drift.
Add interpretability so teams and regulators can understand model outputs.
Explainability is required for audits and remediation—especially where automated decisions affect customers.
Rules engine and orchestration
A rules engine captures deterministic policies and business logic. Good engines provide:
Rule versioning and testing.
Sandboxed evaluation against historical data.
Orchestration capabilities to trigger actions across systems (payments, account services, CRMs).
Rules and models should work in tandem: use rules for fixed compliance constraints and ML for probabilistic detection.
Case management and investigator tooling
Case management centralises context for investigations. Essential features:
Aggregated event timelines, linked entities, and evidence.
Task assignment, SLAs, and prioritisation.
Audit logs and collaboration notes.
Workflow automation for routine tasks.
A strong investigator UX reduces time-to-resolution and improves accuracy.
Analytics, dashboards, and reporting
Analytics translate alerts into oversight and continuous improvement:
Dashboards for operational health, trends, and model performance.
Root cause analysis and drill-downs for spikes.
Reporting templates for regulators and management.
Actionable analytics drive rule tuning and model retraining.
Integration, APIs, and data ingestion
A fraud solution must ingest signals from payment processors, application logs, identity providers, device and network telemetry, and third-party risk feeds. Integration capabilities should include:
Event streaming (Kafka, webhooks) and batch ingestion.
Real-time decisioning APIs for external systems.
Secure, well-documented connectors to common identity and payments services.
Standardised data schemas reduce integration complexity.
Device intelligence and behavioral analytics
Device intelligence collects device fingerprints, browser and OS attributes, IP reputation, and geo-location. Behavioral analytics assess user interactions—navigation patterns, typing cadence, or mouse movement—to detect anomalies. These signals reduce false positives while identifying sophisticated attacks.
Identity verification and enrichment
Identity verification combines document checks, biometric comparisons, and third-party data enrichment. Features to evaluate:
Multiple verification methods (document OCR, liveness checks, database matches).
Watchlist and sanctions screening.
Risk-based verification flows to limit friction.
Verify as much as needed for the risk level; excessive checks hurt conversion and privacy.
Compliance reporting and auditability
The platform must support AML and KYC compliance with:
Tamper-evident logs and exportable reporting.
Support for suspicious activity reports (SARs) and regulator data requests.
Retention policies aligned with local rules.
Benefits for business and operations
A well-implemented solution produces measurable benefits:
Reduced fraud losses: Faster detection and response shrink exposure.
Fewer false positives: Better context and scoring reduce customer friction.
Increased operational efficiency: Automation and better tools reduce manual workload.
Scalable investigations: Platforms enable higher throughput for the same team.
Improved compliance posture: Audit trails and reporting streamline regulator interactions.
Better customer experience: Risk-based decisions minimise unnecessary friction.
These benefits translate to saved costs, preserved revenue, and sustained customer trust.
Deployment and architecture options
Different organisations choose different deployment models based on regulatory, security, and operational constraints.
SaaS: Rapid deployment, lower upfront cost, and vendor-managed updates. Good if you prefer operational simplicity and vendor expertise.
On‑premises: Greater control and data residency options; requires internal ops and infrastructure.
Hybrid: Sensitive data remains on-premises; analytics and models run in the cloud. Balances control with scalability.
Build vs Buy: Building gives full control but requires ongoing investment in data science, engineering, and compliance. Buying accelerates time-to-value but requires careful vendor evaluation.
Each model involves trade-offs in cost, speed, compliance, and control.
Implementation considerations
Technology matters, but people, process, and data drive outcomes. Key considerations:
Data quality and instrumentation
Detection accuracy depends on consistent, complete event data. Steps to prepare:
Standardise event schemas and timestamps across services.
Ensure consistent logging for payments, authentication, and account changes.
Instrument enrichment sources (IP, device, external risk feeds).
Incomplete or inconsistent data is a common root cause of poor detection.
Model lifecycle and feedback loops
Effective ML requires labelled data and continuous feedback:
Implement a development lifecycle: train → validate → test → deploy.
Monitor for performance degradation and bias.
Feed investigator outcomes back into training datasets.
A documented model governance process helps with audits.
Integration testing and latency
Map end-to-end data flows and test under load. Validate:
Latency requirements for decisioning endpoints.
Error handling and retry logic for integrations.
Data reconciliation between systems.
Real-world load tests reveal timing and scaling issues.
Regulatory alignment and explainability
Understand local AML, KYC, and data protection requirements. Ensure:
Audit-ready evidence for suspicious activity.
Documentation showing how automated decisions are reached.
Retention and data export capabilities aligned with rules.
Involve legal and compliance teams early in design.
Privacy and data governance
Adopt privacy-by-design measures:
Limit data retention to what’s necessary.
Apply role-based access controls.
Encrypt data in transit and at rest.
Have clear deletion and export processes.
Privacy constraints often affect architecture choices and feature availability.
Staffing and change management
Plan for roles and training:
Data engineers for integration and pipelines.
Data scientists to build and maintain models.
Investigators and analysts to run operations.
Compliance and legal for regulatory needs.
Provide training, playbooks, and clear SLAs for team coordination.
Operational playbooks and processes
Documented playbooks standardise responses and improve outcomes.
Example investigation workflow
Alert generation: a rule or model flags an event.
Triage: automatic prioritisation; low-risk items auto-close.
Enrichment: fetch transaction history, device data, and identity checks.
Case assignment: route to an investigator with suggested actions.
Decision: confirm fraud, mark false positive, or escalate.
Action: block account, reverse payment, file SAR, notify customer, or close case.
Feedback: record outcome and update models/rules.
Consistency reduces resolution time and ensures auditability.
Escalation paths and SLAs
Define escalation triggers (value thresholds, regulatory exposures) and SLAs for escalation response. Clear ownership between fraud, payments, compliance, and legal teams is essential.
Feedback loops
Capture investigator outcomes and use them to:
Retrain models.
Adjust rule thresholds and logic.
Improve enrichment data sourcing.
Feedback loops close the learning cycle and reduce repeat errors.
Buying checklist
Evaluate vendors or internal builds against this checklist.
Capabilities
Real-time scoring and low-latency decision APIs.
ML models plus interpretability/explainability tools.
Flexible rules engine with versioning and sandbox testing.
Robust case management and investigator workflows.
Integration and data
Event streaming support (Kafka, webhooks).
Connectors for payments, identity providers, and third-party risk feeds.
Secure API for decisioning and enrichment.
Performance and reliability
Low-latency under peak load.
High availability and disaster recovery.
Clear SLAs for uptime and support.
Security and governance
Encryption in transit and at rest.
Role-based access controls and audit logs.
Data retention and export policies.
Compliance and explainability
Support for AML/KYC workflows and SAR exports.
Model explainability and audit trails.
Commercial and operational
Transparent pricing and predictable costs at scale.
Onboarding and integration support.
Data portability and clean exit terms.
KPIs, ROI examples, and measurement
Track practical metrics to measure program health:
Key KPIs
Fraud loss rate: value lost to fraud / total processed value.
Detection rate: share of fraud detected by the system.
False positive rate: alerts closed as non-fraud.
Time to detection: time from event to detection.
Time to resolution: time from alert to closure.
Investigator throughput: cases closed per investigator.
Operational cost per case.
Example ROI calculation (illustrative)
Annual transaction volume: $100m.
Current fraud loss: 0.5% = $500,000.
Expected reduction after solution: 40% → $200,000 saved.
Efficiency savings from automation: $100,000.
Total estimated benefit: $300,000/year.
Annual solution cost (SaaS + integrations + staffing): $120,000.
Net benefit: $180,000; ROI = 150%.
Document baseline metrics and track post-deployment to validate assumptions.
Common pitfalls and mitigation
Overreliance on static rules: combine rules with ML and continuous learning.
Poor data coverage: prioritise instrumentation and consistent schemas.
Ignoring investigator experience: build or choose tools that simplify workflows.
Insufficient model explainability: adopt interpretable methods and explanation layers.
Long integration cycles: map dependencies early and use standard schemas.
Weak governance: establish model, data, and change management processes.
Privacy oversights: enforce minimisation, access control, and retention limits.
Mitigation requires combining technical fixes with strong process controls and cross-functional collaboration.
Maintaining and evolving the program
Fraud risk evolves; so should your program. Regular activities include:
Quarterly rule reviews and retirement of stale rules.
Scheduled model retraining and validation.
Routine playbook updates and investigator training.
Post-incident reviews and root-cause analysis.
Periodic vendor and tech stack reassessments.
A steady cadence keeps detection accurate and controls current.
Closing: choosing a partner that helps you stay ahead
Selecting a fraud management solution is both a technical and organisational decision. The right platform integrates reliably with your systems, provides explainable detection, supports investigator workflows, and aligns with regulatory needs. It’s not a one-time purchase—it’s a long-term capability that requires continuous data quality, disciplined governance, and close collaboration between risk, compliance, and engineering teams.
At Pingwire, we focus on clarity, reliability, and measurable outcomes. We design platforms that prioritise explainability, integration, and investigator productivity to help teams detect threats in real time while keeping customer friction low. Evaluate vendors and internal builds against the criteria and operational practices described here to choose a solution that protects customers, supports compliance, and scales with your business.